BlogSafe.org

WordPress Security Tools, Research, and Recovery

Diagnostics, vulnerability tracking, and abandoned plugin monitoring built around a safer WordPress ecosystem.

!
Find Risks Early

Identify vulnerabilities, misconfigurations, and abandoned plugins before they become larger problems.

✓
Keep Sites Safer

Tools and research for site owners, developers, and agencies.

▥
A Healthier WordPress Ecosystem

More transparency, better tools, and less abandoned code.

Debug 360 by BlogSafe
Free plugin

Your debug.log is a public file. Debug 360 fixes that.

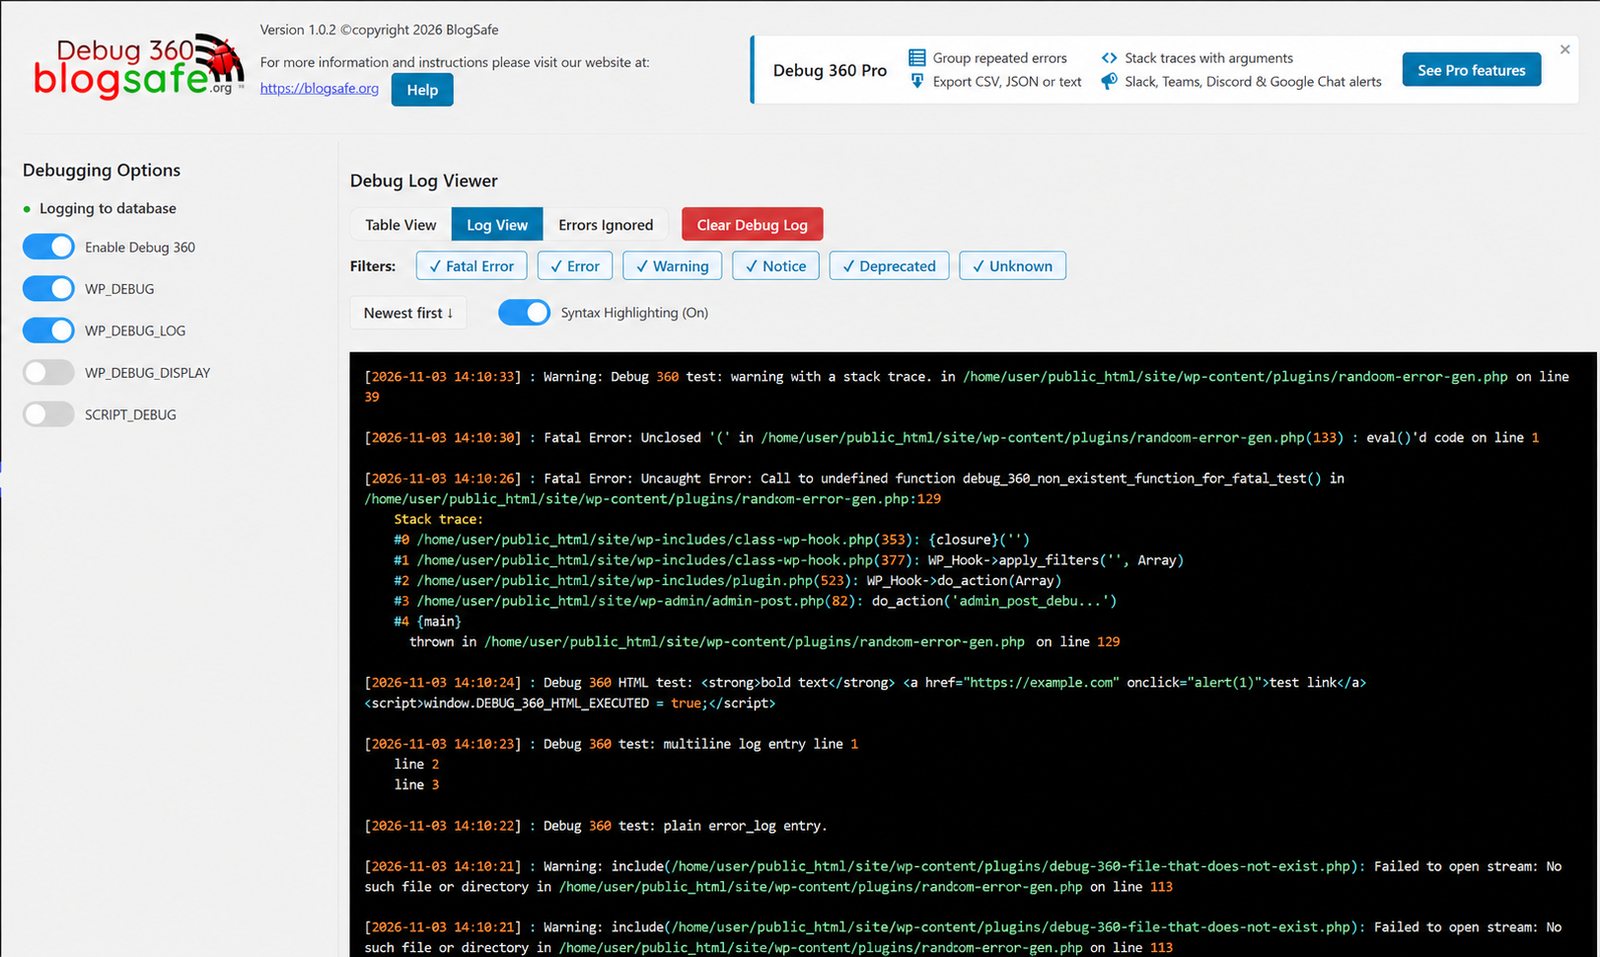
Debug 360 isn't a log reader. Its own PHP error handler and shutdown handler send errors straight into your WordPress database instead of a file anyone can download, and you read them in a fast, clear log in your admin.

  • Its own error and shutdown handlers catch errors as they happen, fatal ones included
  • Ignore the noise you can’t fix
  • Email alerts when something breaks

Debug 360 Pro adds grouped errors, stack traces and Slack, Teams, Discord & Google Chat alerts for $49.00 USD, with a 30-day money-back guarantee. See Pro

The Debug 360 log: PHP errors with their time, colour-coded, beside the debugging switches

Live vulnerability data

Latest WordPress CVEs

22,920 vulnerability records currently indexed.

View all CVEs
CVE-2026-96841 November 18, 2026
The ITRO Popup Plugin plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'custom_html' parameter in all versions up to, and including, 5.2.6 due to insufficient input sanitization and output escaping. This… Full details
MEDIUM 6.4
CVE-2026-96665 November 18, 2026
The SendPress Newsletters plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'sp_firstname' parameter in all versions up to, and including, 1.26.1.20 due to insufficient input sanitization and output escaping. This makes… Full details
HIGH 7.2
CVE-2026-92535 November 18, 2026
The Make Connector plugin for WordPress is vulnerable to Sensitive Information Exposure in all versions up to, and including, 1.6.6 via the include_custom_fields. This makes it possible for unauthenticated attackers to extract arbitrary admin-selected… Full details
MEDIUM 5.3
CVE-2026-109619 October 21, 2026
PHP has various global state that temporarily points into request memory. In some scenarios, global state may not be correctly reset, or may be repopulated after being reset. The global state may then refer… Full details
CRITICAL 9.2
CVE-2026-109618 October 21, 2026
PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request. Some contexts may not properly account for this scenario and leave request memory in an uninitialized… Full details
CRITICAL 9.2
CVE-2026-92842 September 25, 2026
The convert.base64-encode, convert.quoted-printable-encode and convert.quoted-printable-decode stream filters accept a line-break-chars option whose length is tracked separately from the string itself. The filter constructors duplicate the value with pestrdup(), which stops at the first NUL… Full details
MEDIUM 5.9

Homeless & Abandoned Plugins

Track unmaintained WordPress plugins, evidence of abandonment, known risks, alternatives, and future rescue work.

Browse Database